
Latest update: As of October 8, ASOS has acknowledged the theft of customer profiles following the BBC’s investigation. The full scale of the breach and the attackers’ claimed method of accessing the data remain under investigation.
LONDON, October 8, 2026 — ASOS has confirmed that hackers stole detailed customer profiles containing names, addresses, phone numbers, email addresses and shopping search histories, after a BBC investigation revealed the cyberattack was more extensive than the online fashion retailer initially disclosed.
The new findings raise concerns for potentially millions of ASOS shoppers, although the company has not confirmed how many accounts were affected. ASOS says passwords and banking details were not accessed, but customers are being warned about phishing emails, fraudulent calls and impersonation scams.
BBC investigation reveals wider ASOS customer data breach
ASOS initially told customers that basic personal information, including names and contact details, might have been accessed during the October 6 cyberattack.
However, BBC News reported on October 8 that cybercriminals had contacted its journalists on Wednesday evening and shared samples of stolen customer records showing that considerably more information had been obtained.
The compromised profiles reportedly include:
- Customer names and residential addresses.
- Phone numbers and email addresses.
- ASOS customer identification numbers.
- Search histories from the ASOS website.
The search data included terms such as “reclaimed vintage”, “glamorous wide fit” and “ASOS petite”.
Although shopping searches may appear relatively harmless, combining them with names and contact information could help criminals create convincing messages tailored to individual customers.
The BBC said it delayed publishing its findings to allow ASOS to contact customers first. The retailer subsequently acknowledged that detailed customer profiles had been taken.
Hackers gained access by impersonating a trusted contact
ASOS has now provided additional information about how the attackers entered its systems.
According to the company’s latest customer communication, cybercriminals gained access to an employee account after impersonating a trusted contact and obtaining login credentials.
Those credentials reportedly allowed the attackers to access an unnamed service and download customer information.
ASOS has not publicly identified the employee, disclosed the specific service involved or confirmed how many customer profiles were downloaded.
Suspicious ASOS app notification exposed the attack
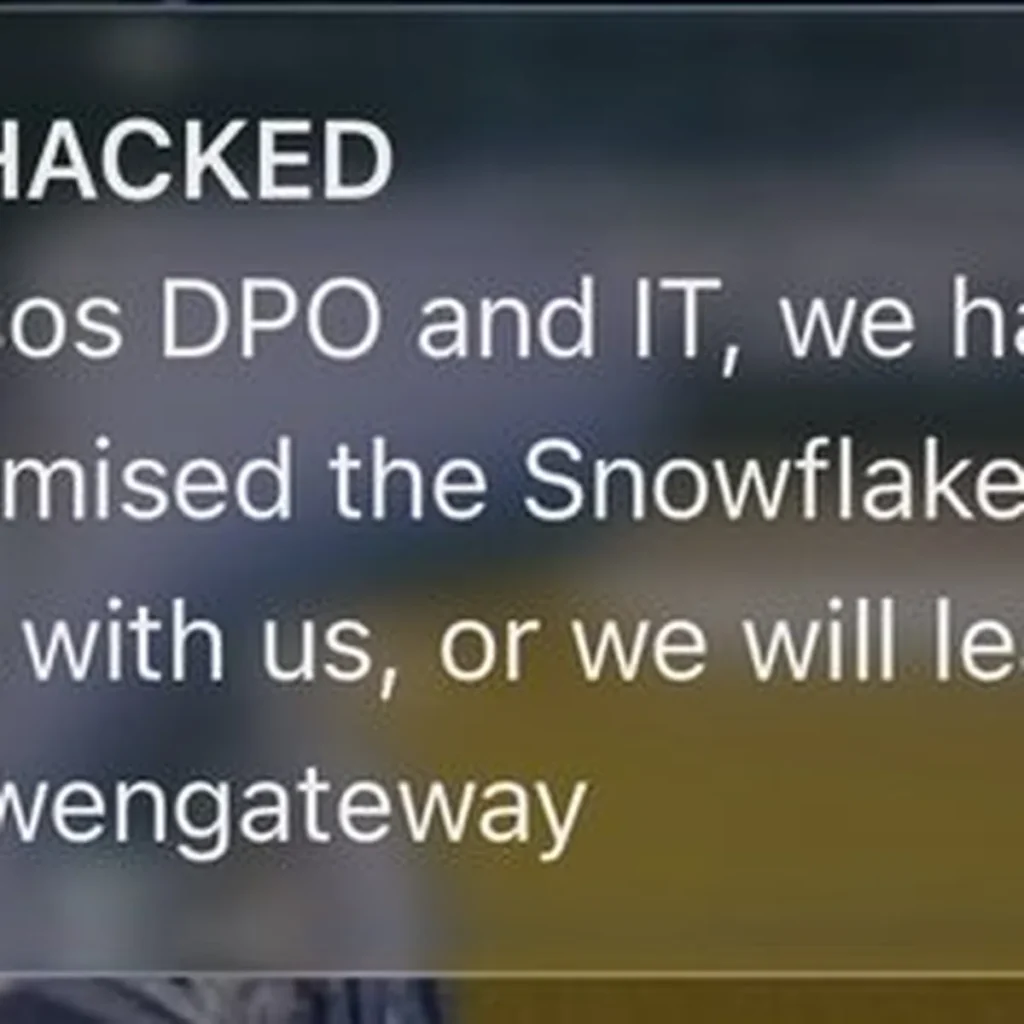
The breach became public on Tuesday, October 6, when shoppers received an unexpected notification through the official ASOS app.
The message was addressed to the company’s data protection officer and IT team and stated:
“Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.”
The notification was particularly concerning because it appeared through a trusted retailer’s own communication system rather than an ordinary phishing email.
BREAKING: ASOS customers have received a push notification saying the e-commerce giant had been ‘hacked’ Sky’s Phoebe Southworth has the details. https://t.co/7BFsCqBOSG https://t.co/4HuvhGLNqk
— Sky News (@SkyNews) October 6, 2026
Later that day, ASOS confirmed through a London Stock Exchange announcement that an unauthorised third party had sent the notification and that customer information might have been accessed.
Xuanyewen hackers claim access through Simon AI and Snowflake
The cybercriminals, identifying themselves to the BBC as Xuanyewen, claimed they obtained the data through Simon AI, a platform built on Snowflake technology.
Snowflake provides cloud-based data storage and analytics services used by businesses worldwide.
However, the attackers’ explanation has not been independently verified. Simon AI was contacted for comment, while Snowflake previously stated that its platform had not been breached.
The distinction is important because criminals accessing a business account through stolen credentials does not necessarily mean the underlying cloud platform itself was compromised.
Investigators have yet to establish whether the same compromised credentials were used to access both customer records and the app notification system.
ASOS confirms passwords and banking details were not stolen
In its latest email to customers, ASOS said the stolen profiles did not include passwords or banking information.
The retailer also confirmed that its website and mobile app remain safe to use and that customers are not currently required to take action.
However, the exposure of genuine personal details increases the risk of criminals impersonating ASOS representatives.
Customers should be particularly cautious about unexpected refund offers, payment requests, account verification messages or warnings that their accounts will be suspended.
Origin Energy Data Breach: 900,000 Customers Affected
Cybersecurity experts warn of convincing phishing scams
Trevor Dearing, senior director of critical infrastructure at Illumio, warned that scammers could use the stolen information to make fraudulent communications appear genuine.
Criminals may reference the ASOS breach, use real customer details and create urgency by threatening to lock accounts within 24 hours.
Shoppers should avoid clicking suspicious links, verify communications through official ASOS channels and consider changing passwords that are reused across other services as a precaution.
ASOS’s official cybersecurity guidance provides additional advice on protecting accounts and recognising suspicious communications.
ASOS shares fall as investors assess cyberattack
ASOS shares dropped by around 12% at one stage following the initial disclosure before recovering some losses.
The incident highlights the financial and reputational risks associated with customer data exposure, particularly when attackers obtain information that could be exploited for targeted fraud.
Other recent cybersecurity incidents, including the Denmark data breach involving CPR records, have also raised concerns about the protection of personal information.
ASOS investigation continues as number of affected customers remains unknown
ASOS says it has taken additional steps to strengthen its security controls and continues to investigate the breach.
The company has not disclosed the total number of affected accounts or confirmed whether additional categories of information were accessed.
For customers, the most important development is that the incident now involves confirmed theft of detailed personal profiles rather than only a suspicious app notification.
Although ASOS says passwords and banking details remain secure, shoppers should remain alert to unexpected messages and calls using their personal information.

Make Swikblog your go-to source on Google for reliable updates, smart insights, and daily trends.